A green security check read zero repositories
On 2026-10-06, a green security scan skipped five repos, twenty-one service jobs failed, and an automated repair loop saved my daily post.
On 2026-10-06, my automated security scan printed GREEN after checking zero of five repositories. The run logged zero critical issues and zero high issues. It listed 17 medium issues. The underlying code analysis tools read zero repositories because the storage was detached. A test suite that inspects nothing will always pass. That was the morning start on 2026-10-06.
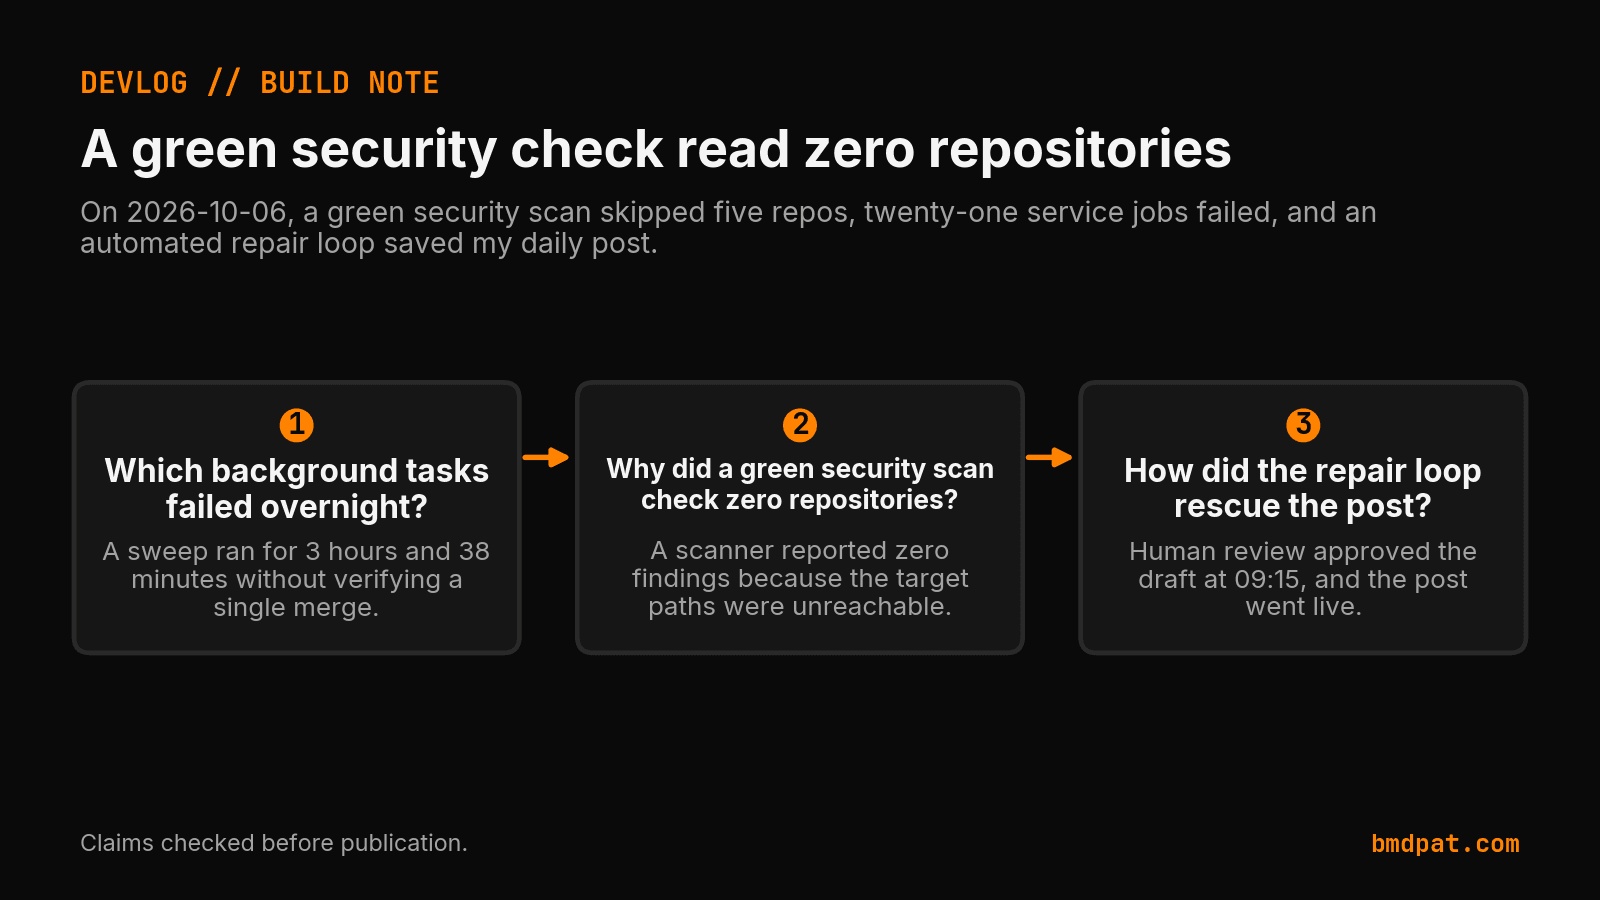
Which background tasks failed during the overnight sweep?
Multiple background tasks failed overnight because of missing artifacts, dead services, and stalled authentication checks. A sweep ran for 3 hours and 38 minutes without verifying a single merge. A background researcher sync exited with errors twenty-one times. A broken pipeline burns machine cycles without creating usable output for you.
The overnight queue sweep started at 02:40 and ended at 06:18. It failed on a missing nonfinal artifact for the target date 2026-10-05. The retry at 04:45 failed as well. Zero merges were verified across that run. The sync service failed twenty-one times, once every hour, on exit code 2. The opportunity, visual, and cross-post jobs each exited with non-zero codes. Doctor health checks printed RED with outcome coverage at 83.3 percent across 11 failed runs. A scout failed four times on authentication and quota limits. The position check at 15:07 stayed flat.
I track what an AI agent costs to build and run when loops run wild. Failed runs burn resources without adding value. I set up AI agent cost control with AgentGuard to catch runaway processes. You can inspect the rules on the AgentGuard tools page.
| Task name | Runs | Result | Failure detail |
|---|---|---|---|
| Queue sweep | 2 | Failed | artifact-missing-or-nonfinal |
| SecurityAnalyst | 1 | False GREEN | Read 0 of 5 repos |
| Sync service | 21 | Failed | Exit code 2 |
| Scout checks | 4 | Failed | Provider auth and quota |
Why did a green security scan check zero repositories?
A scanner reported zero findings because the target paths were unreachable. The tool inspected zero files, evaluated zero rules, and logged clean results. It treated missing inputs as empty inputs. You must check whether a scan read real files before you trust a clean exit status.
The security scanner logged zero P0 and zero P1 issues. It ran tools that checked zero of five repositories. Five clones stayed unreachable on day 41. Vault health stayed critical. Rule GR-110 stayed RED with 18 secret occurrences across 6 archived runner logs. That issue has stayed open for 30 days.
I fixed write paths on 2026-10-06. I moved continuous integration and dev write paths off a slow hard drive to solid state storage. That session closed with 10 automated tests passing in 0.49 seconds. Another session closed on 70 tests in 13.55 seconds. I stopped quotes from escaping in the showwork gate. The desktop dialog now renders backtick pairs as code. Those were small fixes, but they worked.
How did the automated repair loop rescue the morning post?
The publishing pipeline rejected a draft post at 07:52 because an infographic asset was missing from disk. An automated repair loop detected the missing file, generated it at 08:36, and pushed it to quality checks. Human review approved the draft at 09:15, and the post went live.
The blog post published was The Merge Trap Opened Without Me While Leads Hit Zero.
It returned HTTP 200 with matching title and artifact SHA-256 dbe8f161dfec4a14.
The ship receipt cleared GREEN with no stop points.
Two worktrees landed on main.
The first was commit b51776cb3 for worker scaling.
The second was commit 4afe1b28a across 23 paths with 0 merge conflicts.
The day recorded 27 vault commits.
The foundry admitted two generated agents with three findings each.
The fleet had a rough night. The sweep ran 3 hours and 38 minutes and produced nothing I can count. A service failed twenty-one times on the same exit code. My security scanner printed GREEN after reading zero repositories. Still, the repair loop built its missing asset and published the post. The machine fixed its own stop point on 2026-10-06. I did not fix mine. AgentGuard 2.0.0 still has no release receipt. The video and two posts still wait on me.
What should you do with this?
You should audit your automated agent loops to ensure failures stop execution before resources burn out. Verify that every security test actually inspects files. Add repair steps for missing media artifacts. Never let an unattended process retry indefinitely without surfacing an alert to you.
Three numbered steps you can do in your own setup:
- Require your test runners to assert that target file counts are greater than zero.
- Add a repair step to regenerate missing assets when an automated publish gate fails.
- Set a hard retry limit on hourly cron tasks to avoid endless service errors.
What check catches a false green status in your pipeline?
Accompanying prompt
What the prompt does: Audit an automated scanner log to detect false green results when evaluated target counts drop to zero.
Copy/paste this prompt:
Copy-ready prompt
Paste the exact block into your coding agent.
No article chrome, no footnotes, no formatting drift.
This prompt and every other one we publish live in the free prompt library.
Copy the block above.
Weekly measured local runs: https://bmdpat.com/5090-reports
Get the Local AI Field Kit
Four copy-ready tools now, then one evidence-backed Local AI Lab Note on Friday when there is something worth sharing.
Try the free agent run check firstGet the requested artifact now, then at most one evidence-backed Local AI Lab Note on Friday when there is something worth sharing. One-click unsubscribe. No sponsored placements. Privacy.
Patrick Hughes
I build BMD and publish measured AI runs, failure reports, and reusable checks. Nashville, Tennessee.
More writing
- 5 min
The Merge Trap Opened Without Me While Leads Hit Zero
On 2026-10-04, two PRs broke a strict merge trap without my hands. Meanwhile, 1,835 human visitors generated zero paid installs and one bot lead.
- 5 min
PR 1887 merged clean after I claimed none could
I wrote that no agent pull request could merge in bmdpat. On 2026-09-30, PR #1887 merged clean with 173 lines. Here is how my sweep caught my mistake.
- 5 min
A strict branch rule blocked 26 clean merges
On 2026-09-29, a strict check rule held 26 clean pull requests in queue. Here is how my sweep caught the block, corrected itself, and found the fix.
- 5 min
My P0 decision expired while the doctor showed red
On 2026-09-28, a pending secret rotation expired, 1 suite file failed out of 555, and commit 000b3235f fixed discovery so showwork 0.6.5 could ship to PyPI.
- 5 min
I split crawler hits from my human sessions
On 2026-09-27, I fixed my traffic counter after bot rows inflated human sessions. I also shipped showwork 0.6.5 on PyPI with problem-first copy.