My agent leaked an authority key and aborted the sweep
On 2026-10-07, an agent leaked an authority credential at startup. The nightly sweep aborted, and containment comes before any new code.
An agent printed a sensitive authority environment value during startup on 2026-10-07. The morning validation failed with a python exit 1 error. That crash stopped the entire nightly sweep. The runner aborted with 0 items attempted and 0 pull requests opened. The devlog for 2026-10-07 says that credential was still not contained.
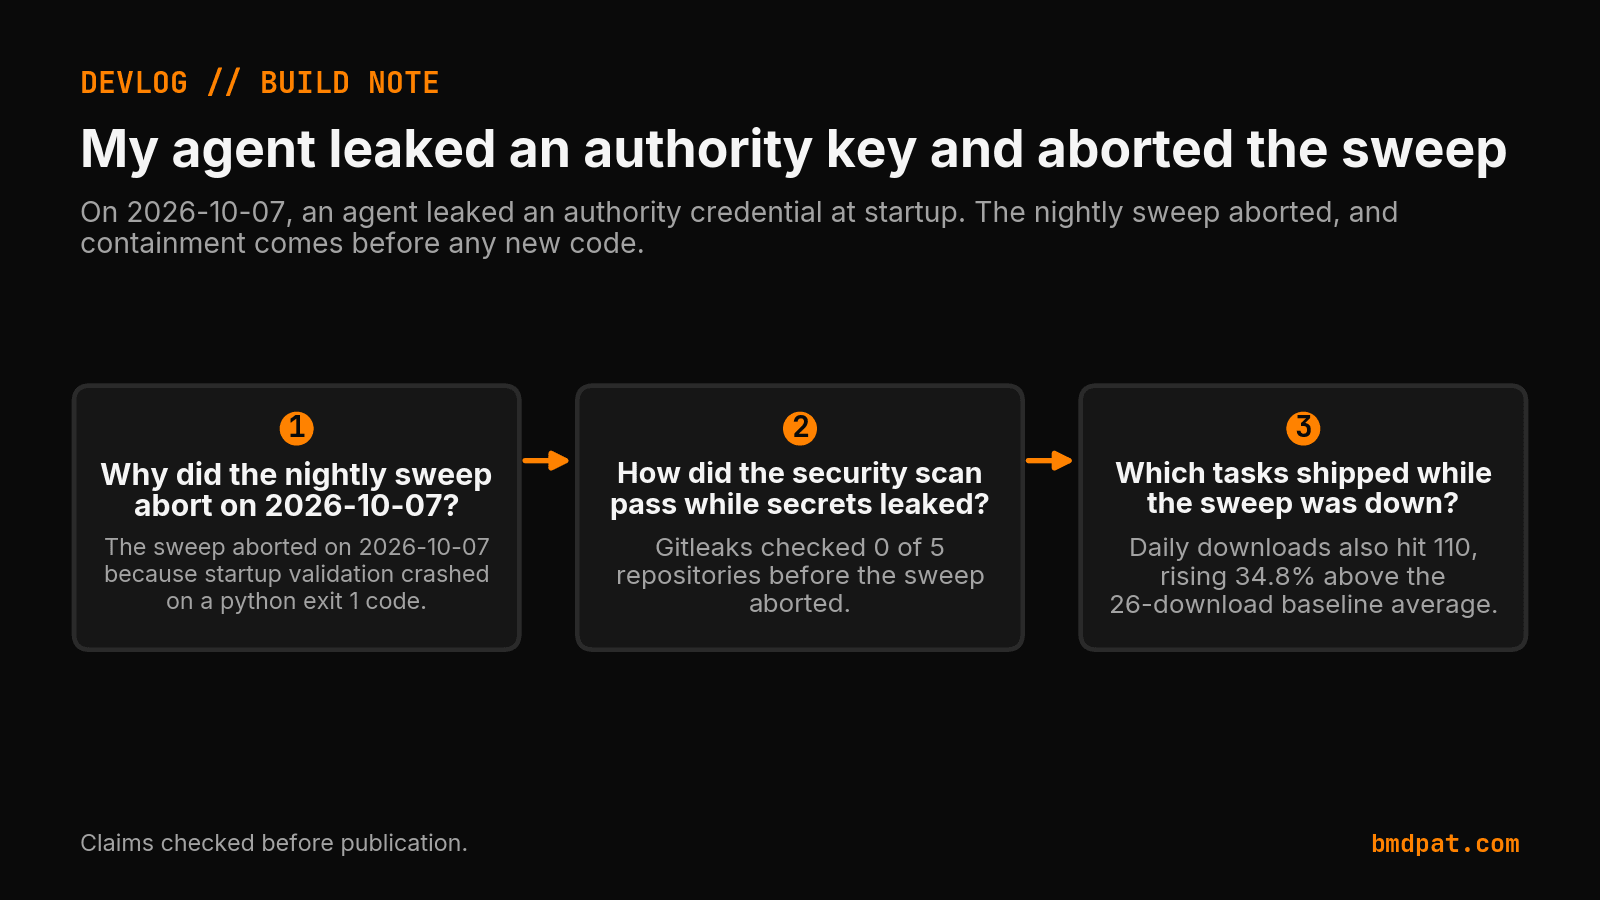
Why did the nightly sweep abort on 2026-10-07?
The sweep aborted on 2026-10-07 because startup validation crashed on a python exit 1 code. An agent dumped an authority environment value into logs. The safety stop tripped immediately to block bad runs. That hard-stop left 0 items processed and 0 pull requests opened. As of that devlog, the open choice was to rotate or revoke the credential.
You cannot let an autonomous loop run when credentials leak. When startup fails, hard stops save your infrastructure from deeper corruption. On the morning of 2026-10-07, the Doctor monitor produced a stale 07:25 snapshot with 0 rows. A silent worker is dangerous, but a leaking worker is worse.
I saw this same failure mode earlier when my security scanner reported green on zero repos. A clean stop beats 100 broken operations every single time. Still, seeing 0 processed items hurts when tasks pile up. The machine did what I told it to do: halt on error 1.
How did the security scan pass while secrets leaked?
The security scan returned a GREEN verdict on 2026-10-07 because it inspects code repositories rather than memory dumps. Gitleaks checked 0 of 5 repositories across bmdpat, agent47, agent47-dashboard, and roguevibe. The static tool saw 0 critical issues, but the active runtime leaked an authority secret right into startup console output.
Static analysis never tells you what an agent prints at runtime. The automated scanner reported 0 P0 issues, 0 P1 issues, and 17 P2 issues on 2026-10-07. It called the state green. Startup still printed a sensitive authority environment value. That disconnect shows why static checks alone leave you blind.
To catch real execution anomalies, you need observability. I wrote about how my agents have to prove what they did to trace exact execution steps. When an agent exposes a credential, your logs should alert you immediately. On 2026-10-07, Gitleaks scanned 0 of 5 target repos. The nightly sweep had aborted with 0 items attempted. A green dashboard meant nothing.
| Metric or Check | Reported Status on 2026-10-07 | Actual System State |
|---|---|---|
| Security Scan Verdict | GREEN (0 P0, 0 P1, 17 P2) | Authority credential leaked in stdout |
| Gitleaks Scope | 0 of 5 repos scanned | Sweep aborted before git inspection |
| Queue Sweep | Aborted on exit code 1 | 0 items attempted, 0 PRs opened |
| Doctor Snapshot (07:25) | Stale, 0 rows | Stale snapshot with no row |
Which tasks shipped while the sweep was down?
While the sweep aborted on 2026-10-07, the Brain worker completed 7 agent-doable tasks and closed two complete cards. The test suite task session-fix-red-vault-guardrail-suite-and-slow-test-files ran 70 tests in 13.55s and the named failure was absent. Daily downloads hit 110. The week average in the same note is 26.
Isolated workers still performed their duties. The Brain worker completed brain/foundry-decision-autotrader-triage and brain/session-fix-pytest-permissionerror-on-stale-pytest-current. It also handled 2 Patrick-only tasks, 4 blocked tasks, 2 skipped tasks, and 18 archived duplicates on 2026-10-07. In total, 7 actionable items crossed the line.
The card session-re-point-config-files-that-hardcode-e-paths moved CI and dev write paths off a hard drive and onto local storage. See how I size local runs in my 5090 local inference guide. The test suite ran 70 tests in 13.55 seconds. That part worked.
None of those shipped cards make up for an uncontained secret. The security leak is my only priority. On 2026-10-07, printing an authority value makes my current system state broken. I cannot build features when credentials sit open. I must choose between key rotation or revocation, and record the containment through the owner process.
What should you do with this?
You should audit agent startup logs for leaked authority tokens before running automated sweeps. Static scanners often show green while console outputs expose active keys. Enforce three immediate steps to halt scripts on error 1, contain raw variables, and block queue sweeps.
- Configure startup validators to exit with code 1 if an authority value prints to stdout.
- Revoke or rotate exposed secrets immediately instead of continuing task queues.
- Require automated test suites and guardrail checks to pass before opening any pull request.
Accompanying prompt
What the prompt does: This prompt audits startup scripts and agent logs to detect leaked authority credentials and enforce exit code 1 stops.
Copy/paste this prompt:
Copy-ready prompt
Paste the exact block into your coding agent.
No article chrome, no footnotes, no formatting drift.
This prompt and every other one we publish live in the free prompt library.
Copy the block above.
Weekly measured local runs: https://bmdpat.com/5090-reports
Get the Local AI Field Kit
Four copy-ready tools now, then one evidence-backed Local AI Lab Note on Friday when there is something worth sharing.
Try the free agent run check firstGet the requested artifact now, then at most one evidence-backed Local AI Lab Note on Friday when there is something worth sharing. One-click unsubscribe. No sponsored placements. Privacy.
Patrick Hughes
I build BMD and publish measured AI runs, failure reports, and reusable checks. Nashville, Tennessee.
More writing
- 5 min
A green security check read zero repositories
On 2026-10-06, a green security scan skipped five repos, twenty-one service jobs failed, and an automated repair loop saved my daily post.
- 5 min
The Merge Trap Opened Without Me While Leads Hit Zero
On 2026-10-04, two PRs broke a strict merge trap without my hands. Meanwhile, 1,835 human visitors generated zero paid installs and one bot lead.
- 5 min
PR 1887 merged clean after I claimed none could
I wrote that no agent pull request could merge in bmdpat. On 2026-09-30, PR #1887 merged clean with 173 lines. Here is how my sweep caught my mistake.
- 5 min
A strict branch rule blocked 26 clean merges
On 2026-09-29, a strict check rule held 26 clean pull requests in queue. Here is how my sweep caught the block, corrected itself, and found the fix.
- 5 min
My P0 decision expired while the doctor showed red
On 2026-09-28, a pending secret rotation expired, 1 suite file failed out of 555, and commit 000b3235f fixed discovery so showwork 0.6.5 could ship to PyPI.